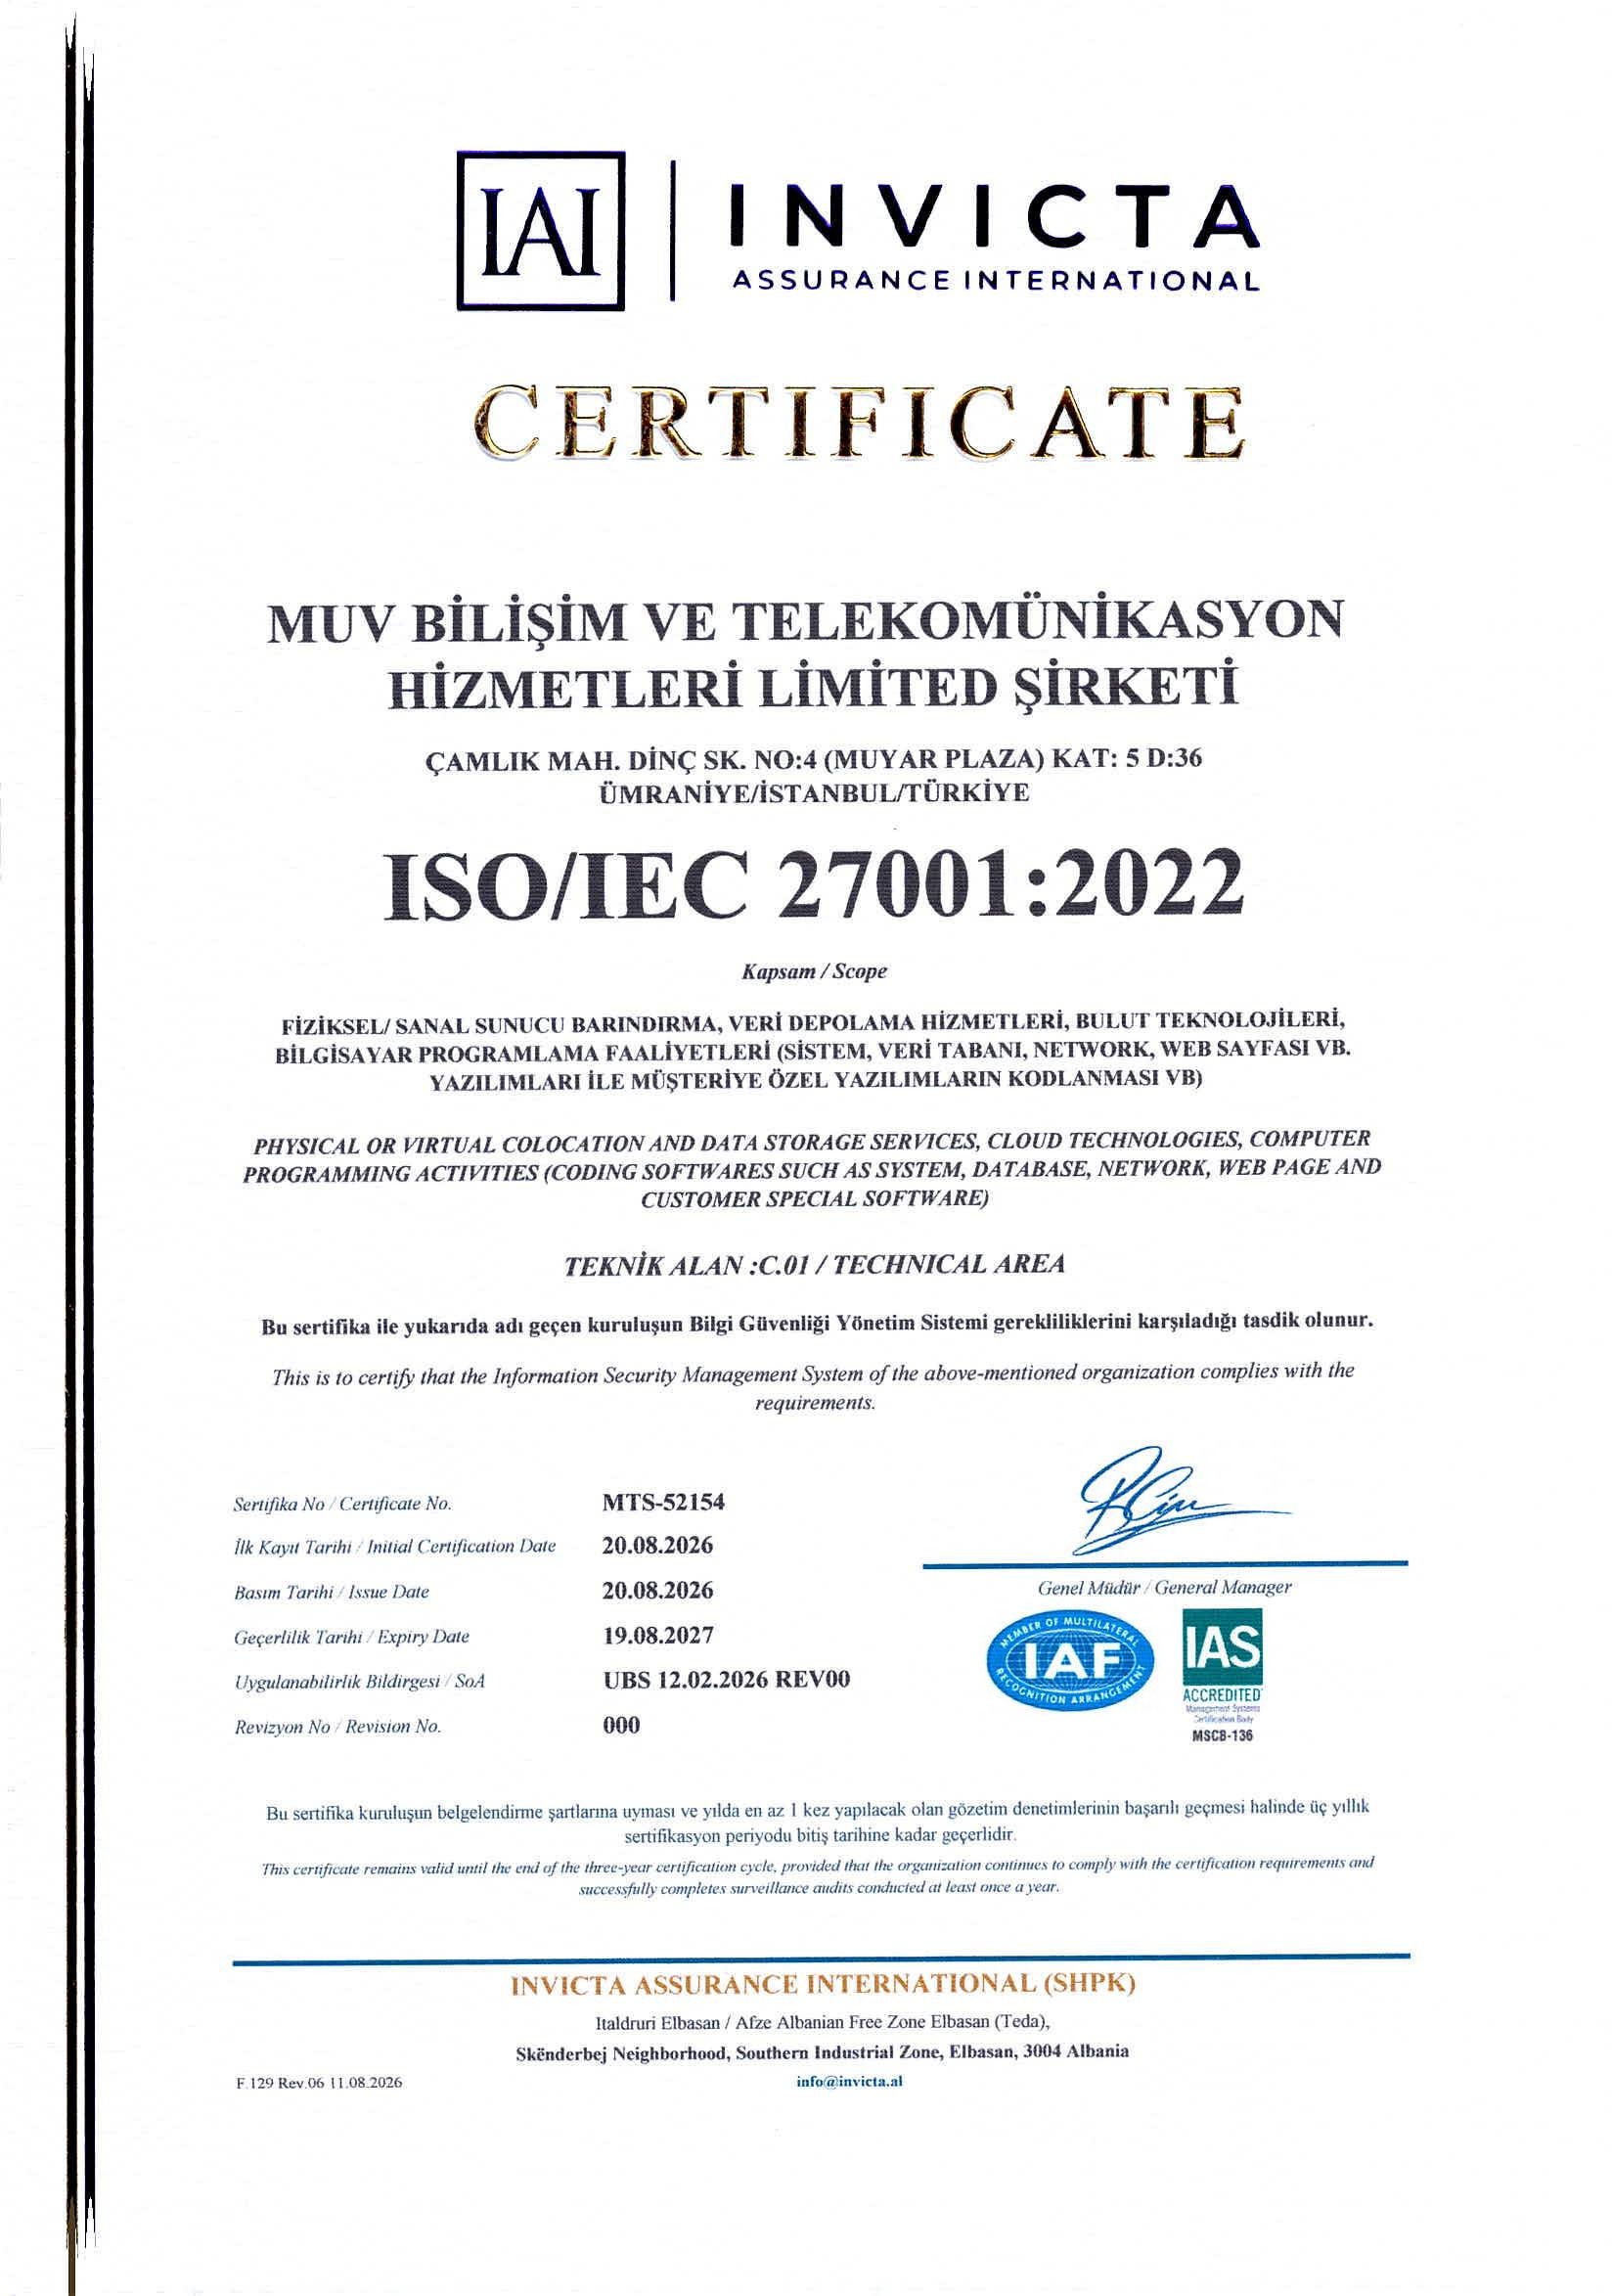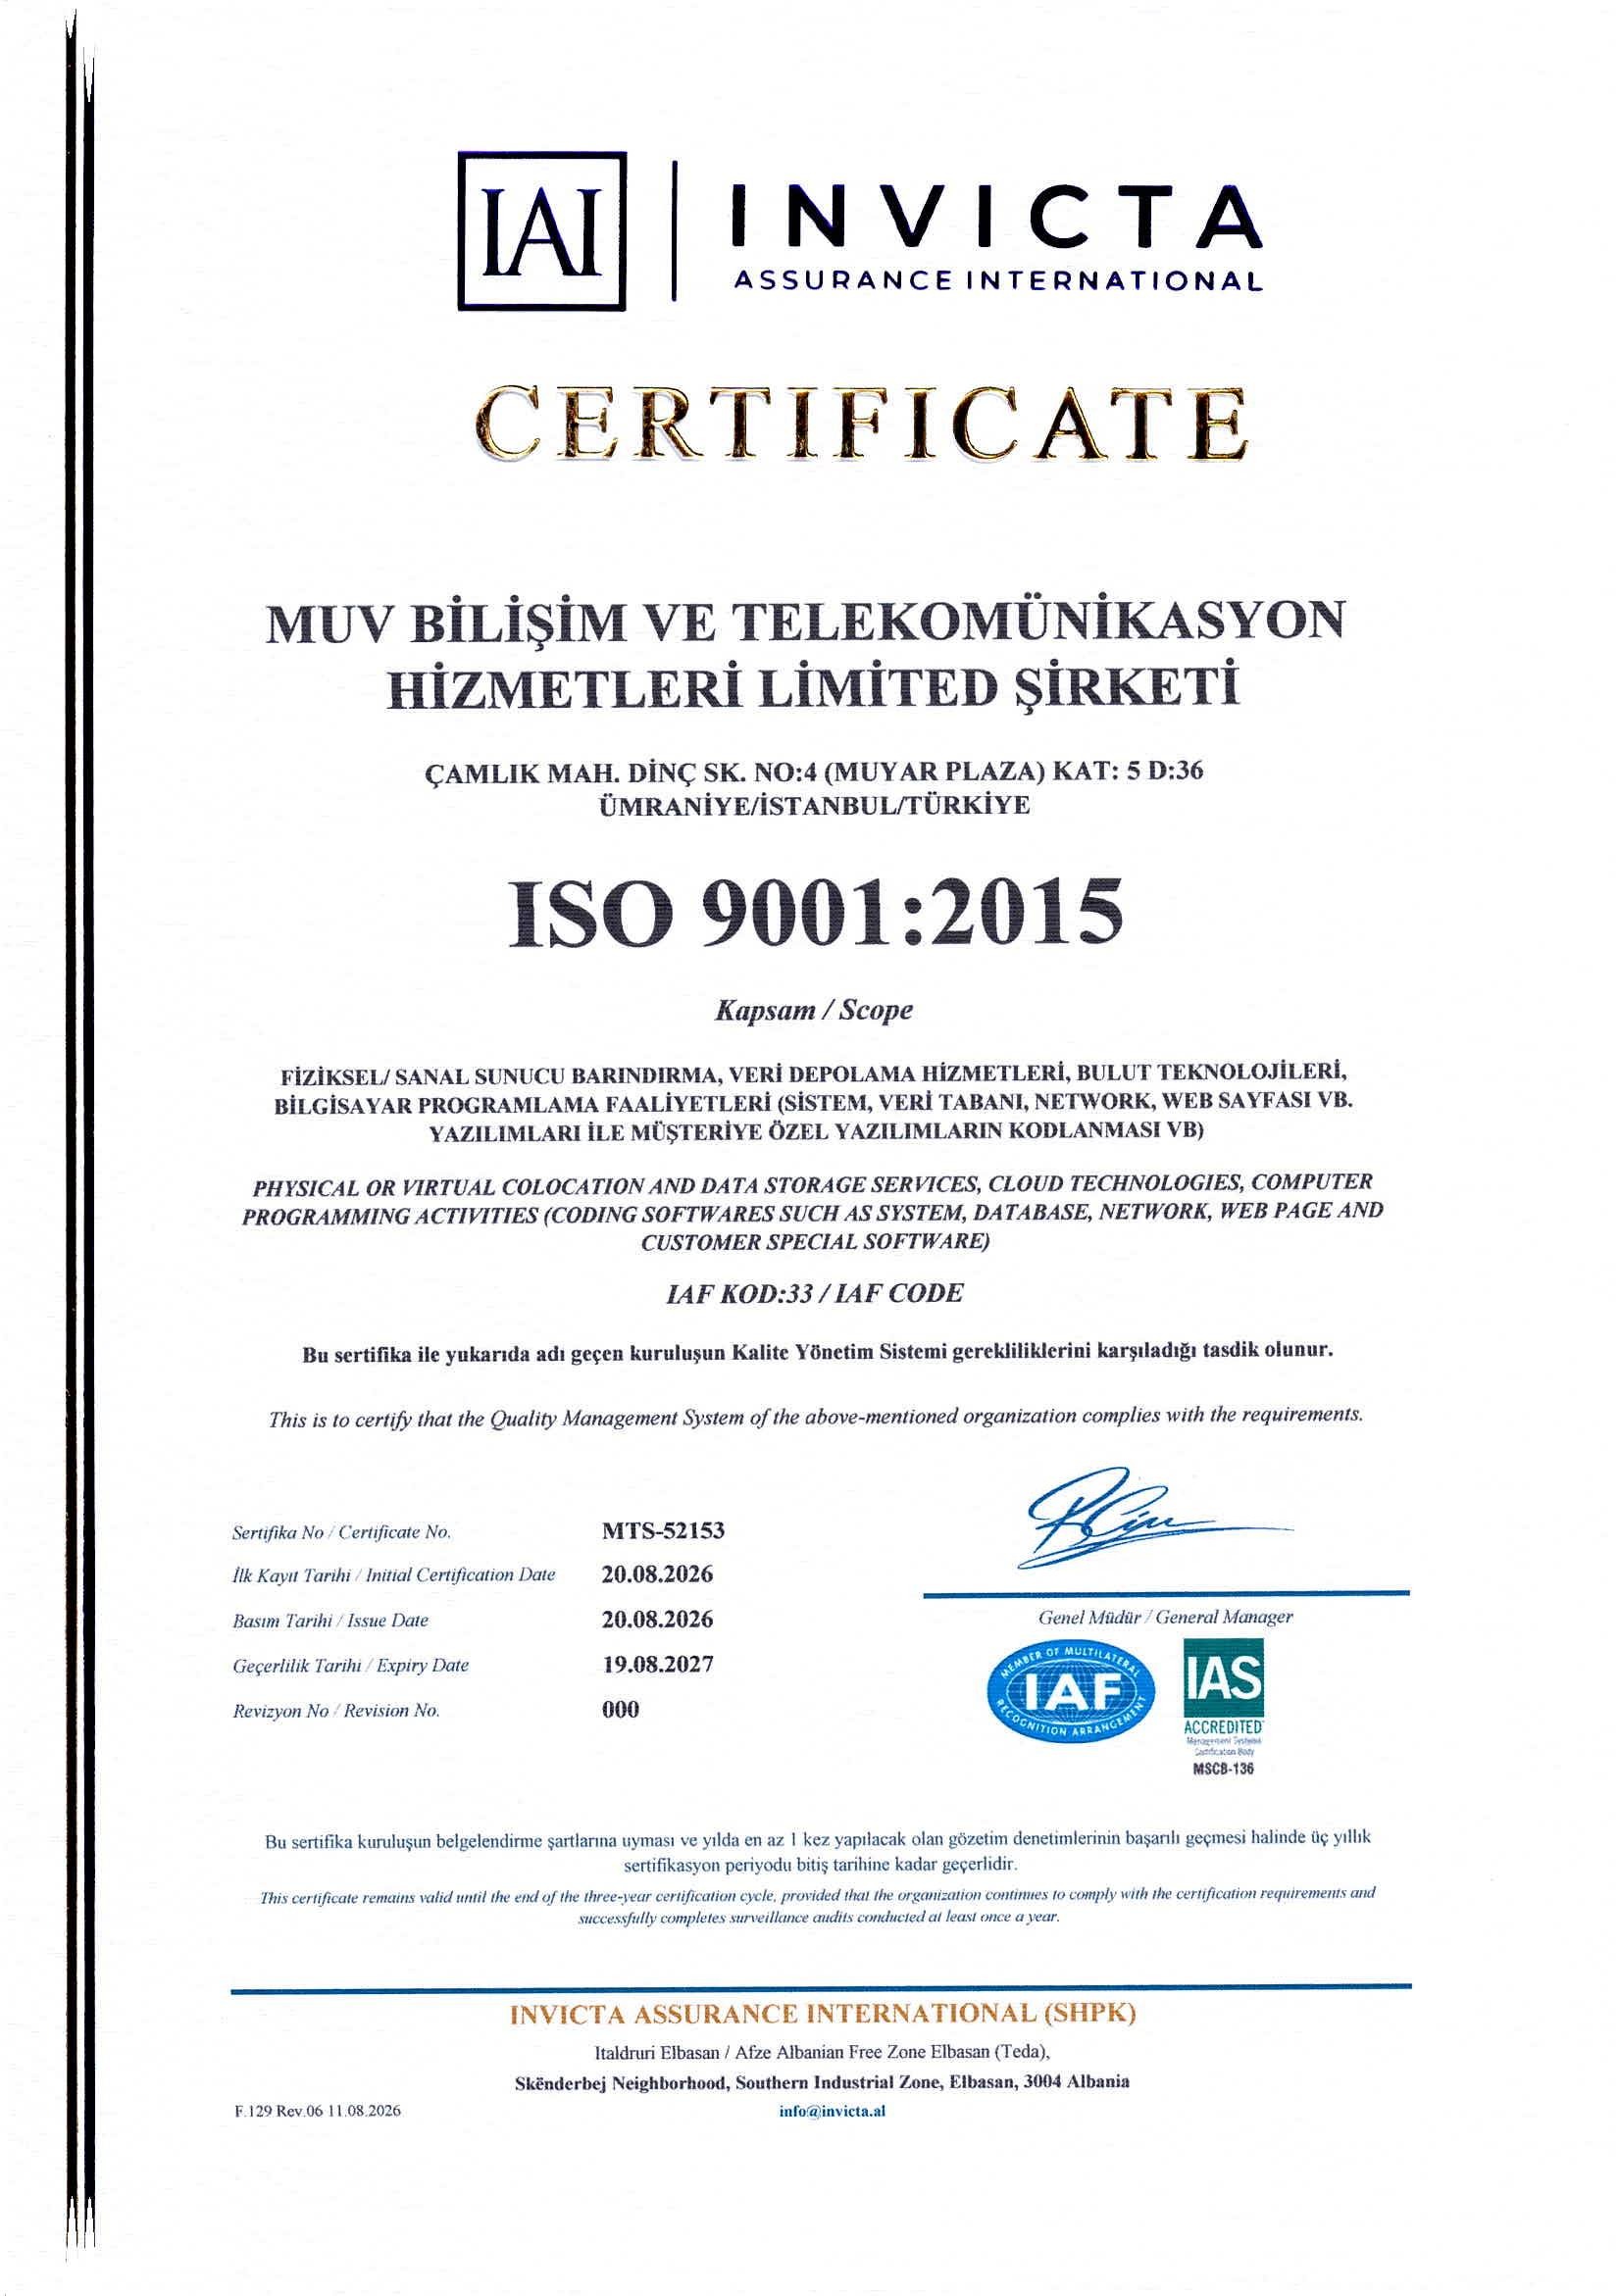

This notice explains, for customers in Turkey, how personal data is stored and deleted, where it is kept, and which technical and organizational measures are used.
1. Purpose
Revive IT Solutions LLC gives priority to processing the personal data of natural persons, including our customers, suppliers, and employees, in line with the Constitution of the Republic of Turkey, the international human-rights treaties to which Turkey is a party, and above all Law No. 6698 on the Protection of Personal Data ("KVKK"), and to making sure that the people whose data is processed can use their rights effectively. These are the rules that apply to customers in Turkey. For that reason, the processing, storage, and transfer of all personal data we obtain in the course of our activities — including, without limitation, data of our employees, suppliers, customers, and users who visit our website and mobile applications — are carried out under the Revive IT Solutions LLC Policy on the Storage and Destruction of Personal Data (the "Policy"). Protecting personal data, and respecting the fundamental rights and freedoms of the natural persons whose personal data is collected, is the basic principle of our policy on processing personal data. We carry out every activity in which personal data is processed with regard for the privacy of private life, the confidentiality of communications, freedom of thought and belief, and the right to an effective remedy. Every administrative and technical protection measure that the nature of the data requires is taken, in line with the legislation and with current technology, to protect personal data. This Policy explains the methods we follow, under the principles set out in the KVKK, when we process, store, transfer, and delete or anonymize personal data shared in the course of our commercial activity, social-responsibility activity, and similar activities. It is the privacy notice for customers in Turkey.
2. Scope
All personal data processed by the Company, including data of our customers, employees, suppliers, and third parties, is within the scope of this Policy. The Policy applies to activities, owned or managed by Revive IT Solutions LLC, in which personal data is processed. It was prepared with regard to the KVKK, the other legislation on personal data, and international standards in this field. It states the rules that apply to customers in Turkey.
3. Definitions
- Recipient group
- The category of natural or legal person to whom the data controller transfers personal data.
- Explicit consent
- Consent that relates to a specific subject, is based on information, and is given freely.
- Employee
- Personnel of Revive IT Solutions LLC.
- Electronic medium
- Media on which personal data can be created, read, changed, and written with electronic devices.
- Service provider
- A natural or legal person who provides a service to MUVCloud under a specific contract.
- Data subject
- The natural person whose personal data is processed.
- Destruction
- Deletion, destruction, or anonymization of personal data.
- Law
- Law No. 6698 on the Protection of Personal Data (KVKK), which sets the rules that apply to customers in Turkey.
- Recording medium
- Any medium on which personal data is kept, whether the data is processed by fully or partly automatic means or, provided it is part of a data-recording system, by non-automatic means.
- Personal data
- Any information relating to an identified or identifiable natural person.
- Personal-data processing inventory
- The inventory data controllers prepare by linking the personal-data processing they carry out, according to their business processes, to the purposes of processing, the data category, the recipient group, and the group of data subjects, and by setting out the maximum period required for the purposes for which the data is processed, the personal data to be transferred abroad, and the measures taken for data security.
- Processing of personal data
- Any operation performed on personal data, such as obtaining, recording, storing, keeping, changing, reorganizing, disclosing, transferring, taking over, making available, classifying, or blocking use, by fully or partly automatic means or, provided it is part of a data-recording system, by non-automatic means.
- Special-category personal data
- Data about a person's race, ethnic origin, political opinion, philosophical belief, religion, sect or other belief, appearance and dress, membership of an association, foundation, or trade union, health, sexual life, criminal conviction and security measures, and biometric and genetic data.
- Policy
- The Policy on the Storage and Destruction of Personal Data (this Policy).
- Data processor
- A natural or legal person who processes personal data on behalf of the data controller, on the authority the data controller gives.
- Data-recording system
- A recording system in which personal data is structured and processed according to specific criteria.
- Data controller
- The natural or legal person who determines the purposes and means of processing personal data and who is responsible for establishing and managing the data-recording system.
- Data Controllers Registry Information System
- The information system, accessible over the Internet, that the Presidency creates and manages and that data controllers use to apply to the Registry and for other registry operations.
- VERBIS
- The Data Controllers Registry Information System.
- Regulation
- The Regulation on the Deletion, Destruction, or Anonymization of Personal Data, published in the Official Gazette on 28 October 2017.
4. Responsibilities and Allocation of Duties
Every unit and employee of Revive IT Solutions LLC actively supports the responsible units so that the technical and administrative measures taken under the Policy are applied properly, so that unit staff are trained and their awareness is raised, monitored, and continually audited, and so that technical and administrative measures are taken in every environment where personal data is processed, in order to prevent unlawful processing of personal data, prevent unlawful access to personal data, and keep personal data in accordance with the law. The Board of Directors is responsible for the senior oversight of setting and operating the notification, review, and sanction mechanisms if the Policy, rules, and regulations are not followed. The policy on the protection and processing of personal data has been approved by the Board of Directors. The Board is the approval mechanism authorized to have the Policy created, applied, and updated when required.
5. Recording Media
| Electronic media | Non-electronic media |
|---|---|
| Physical and virtual servers | Printed documents and paper |
| QNAP backup units | |
| External disks and USB disks | |
| Software developed for MUVCloud | |
| Third-party software | |
| Mobile devices | |
| Printers, scanners, and photocopiers | |
| Other data-recording devices |
6. Legal Grounds That Require Storage
Personal data processed in the course of Revive IT Solutions LLC's activities is kept for the period required by the relevant legislation. For customers in Turkey, that legislation includes:
- Law No. 6698Law on the Protection of Personal Data
- Law No. 6098Turkish Code of Obligations
- Law No. 4734Public Procurement Law
- Law No. 5510Social Insurance and General Health Insurance Law
- Law No. 5651Law on the Regulation of Publications on the Internet and Combating Crimes Committed by Means of Such Publications
- Law No. 6331Occupational Health and Safety Law
- Law No. 4857Labor Law
- Law No. 2547Higher Education Law
- Law No. 2828Social Services Law
- Regulation on Health and Safety Measures to Be Taken in Workplace Buildings and Annexes
- Regulation on Archive Services
Data is kept for the retention periods set by the other secondary legislation in force under these laws. These are the rules that apply to customers in Turkey.
7. Processing Purposes That Require Storage
- Carrying out audit and ethics activities
- Carrying out human-resources processes
- Carrying out training activities
- Carrying out activities in accordance with the legislation
- Carrying out finance and accounting work
- Carrying out internal audit, investigation, and intelligence activities
- Carrying out communication activities
- Preparing statistical studies
- Providing physical and environmental security
- Carrying out and supervising business activities
- Managing call-center processes
- Managing the organization and events
- Carrying out contract processes
- Giving information to authorized persons, institutions, and organizations
- Carrying out management activities
- Making statutory reports
- Carrying out information-security activities
8. Grounds That Require Destruction
Personal data is destroyed in the following cases. These are the rules that apply to customers in Turkey:
- The legislation that was the basis for processing is amended or repealed
- The purpose that required processing or storage no longer exists
- Where personal data is processed only on the condition of explicit consent, the data subject withdraws that consent
- The Authority accepts an application the data subject makes, under Article 11 of the Law, for deletion or destruction of personal data
- The data subject complains to the Board because the Authority rejected an application for deletion, destruction, or anonymization, because the data subject finds the answer insufficient, or because the Authority did not answer within the period set in the Law, and the Board finds the request justified
- The maximum period that required the personal data to be stored has passed, and there is no condition that justifies keeping the personal data for longer
In these cases, on the data subject's request, the Company deletes or destroys the data, or deletes, destroys, or anonymizes it of its own motion.
9. Technical and Administrative Measures
Revive IT Solutions LLC takes technical and administrative measures, within the adequate measures the Board has determined and announced for special-category personal data under the fourth paragraph of Article 6 of the Law, and under Article 12 of the Law, so that personal data is stored securely, is not processed or accessed unlawfully, and is destroyed in accordance with the law. These are the rules that apply to customers in Turkey. The technical measures taken for the personal data processed are listed below:
- Risks and threats that could affect the continuity of information systems are monitored continuously, through real-time analysis in information-security incident management.
- Access to information systems and authorization of users are managed through an access and authorization matrix and through security policies on the corporate active directory.
- The measures required for the physical security of information-system equipment, software, and data are taken.
- Hardware measures (an access-control system that admits only authorized staff to the system room, a monitoring system that runs 24/7, physical security of the edge switches that form the local network, a fire-suppression system, an air-conditioning system, and similar measures) and software measures (firewalls, attack-prevention systems, network access control, systems that block malicious software, and similar measures) are taken so that information systems remain secure against environmental threats.
- Risks of unlawful processing of personal data are identified, technical measures suited to those risks are taken, and technical checks of the measures are carried out.
- Access procedures are created inside the Company, and reporting and analysis are carried out on access to personal data.
- Access to storage areas that hold personal data is logged, and inappropriate access or access attempts are kept under control.
- The Company takes the measures required so that deleted personal data cannot be accessed or reused by the relevant users.
- The Company has set up a system and infrastructure to notify the data subject and the Board if personal data is obtained by others unlawfully.
- Security vulnerabilities are tracked, suitable security patches are installed, and information systems are kept up to date.
- Strong passwords are used in the electronic environments where personal data is processed.
- Secure logging systems are used in the electronic environments where personal data is processed.
- Data-backup programs that store personal data securely are used.
- Access to personal data stored in electronic or non-electronic environments is limited according to access principles.
- Access to the Company's website uses a secure protocol (HTTPS) and is encrypted with the SHA 256-bit RSA algorithm.
- A separate policy has been set for the security of special-category personal data.
- Employees who take part in processing special-category personal data have been trained on the security of that data, confidentiality agreements have been made, and the authority of users who may access the data has been defined.
- Electronic environments in which special-category personal data is processed, kept, or accessed are kept by cryptographic methods, cryptographic keys are kept in secure environments, all transaction records are logged, security updates of the environments are followed continuously, and the required security tests are carried out regularly and their results are recorded.
- Adequate security measures are taken for the physical environments in which special-category personal data is processed, kept, or accessed, physical security is provided, and unauthorized entry and exit are prevented.
- If special-category personal data must be transferred by email, it is transferred in encrypted form with a corporate email address or a KEP account. KEP is the registered electronic mail system used for customers in Turkey. If it must be transferred on portable memory, a CD, a DVD, or a similar medium, it is encrypted by cryptographic methods and the cryptographic key is kept in a different medium. If it is transferred between servers in different physical environments, the transfer is made by establishing a VPN between the servers or by sFTP. If it must be transferred on paper, the measures required against theft, loss, or viewing by unauthorized persons are taken, and the document is sent marked confidential.
10. Administrative Measures
The administrative measures Revive IT Solutions LLC takes for the personal data it processes are listed below:
- Training is given to develop employees' competence, covering prevention of unlawful processing of personal data, prevention of unlawful access to personal data, retention of personal data, communication techniques, technical knowledge and skill, and, where they are part of the rules that apply to customers in Turkey, Law No. 657 and the other relevant legislation.
- Employees sign confidentiality agreements for the activities Revive IT Solutions LLC carries out.
- A disciplinary procedure has been prepared for employees who do not follow the security policies and procedures.
- Before personal-data processing begins, the Company meets its duty to inform the data subjects.
- A personal-data processing inventory has been prepared.
- Periodic and random audits are carried out inside the Company.
- Information-security training is given to employees.
11. Destruction Techniques for Personal Data
At the end of the period set in the relevant legislation, or of the retention period required for the purpose for which the data was processed, the Company destroys personal data of its own motion, or on the data subject's application, by the techniques below and in line with that legislation. These are the rules that apply to customers in Turkey.
12. How Personal Data Is Deleted
Personal data is deleted by the following methods.
| Data recording medium | Description |
|---|---|
| Personal data on servers | For personal data on servers whose required retention period has ended, the Technical Support Team removes the relevant users' access and deletes the data. |
| Personal data in an electronic environment | Personal data in an electronic environment whose required retention period has ended is made inaccessible and unusable for employees other than authorized employees (the relevant users). |
| Personal data in a physical environment | Personal data kept in a physical environment whose required retention period has ended is made inaccessible and unusable for employees. It is also obscured by being crossed out, painted over, or erased so that it cannot be read. |
| Personal data on portable media | Personal data kept on flash-based storage whose required retention period has ended is encrypted by the Technical Support Team, access is given only to the system administrator, and it is kept in secure environments with the encryption keys. |
13. How Personal Data Is Destroyed
Revive IT Solutions LLC destroys personal data by the following methods.
| Data recording medium | Description |
|---|---|
| Personal data in a physical environment | Personal data on paper whose required retention period has ended is destroyed irreversibly by burning. |
| Personal data on optical or magnetic media | Personal data on optical or magnetic media whose required retention period has ended is physically destroyed, including by wiping or by breaking the media. |
14. Anonymization of Personal Data
Anonymization of personal data means bringing personal data to a state in which it cannot be associated with an identified or identifiable natural person by any means, even if it is matched with other data. For personal data to have been anonymized, it must be impossible to associate it with an identified or identifiable natural person even if the data controller or a third party uses techniques that are suitable for the recording medium and the relevant field of activity, such as reversing the data or matching it with other data.
15. Retention and Destruction Periods
For personal data processed in the course of its activities, Revive IT Solutions LLC applies the following retention and destruction periods. For customers in Turkey, these periods follow the rules that apply under the KVKK:
- Retention periods for each item of personal data, for activities carried out according to the processes, are set out in the Personal Data Processing Inventory.
- Retention periods by data category are recorded in VERBIS.
- Retention periods by process are set in the Policy on the Storage and Destruction of Personal Data.
Personal data whose retention period has ended is deleted, destroyed, or anonymized by management of its own motion.
Retention and Destruction Periods By Process
| Process | Retention period | Destruction period |
|---|---|---|
| Preparation of contracts | 10 years after the contract ends | At the first periodic destruction after the retention period ends |
| Carrying out human-resources processes | 10 years after the activity ends | At the first periodic destruction after the retention period ends |
| Log-record tracking systems | 10 years | At the first periodic destruction after the retention period ends |
| Carrying out hardware and software access processes | 2 years | At the first periodic destruction after the retention period ends |
| Records of visitors and meeting participants | 2 years after the event ends | At the first periodic destruction after the retention period ends |
16. Periodic Destruction Interval
Under Article 11 of the Regulation, which is one of the rules that apply to customers in Turkey, Revive IT Solutions LLC has set the periodic destruction interval at 1 year. Periodic destruction is carried out each December.
17. Storage and Publication of the Policy
The Policy is published electronically by Revive IT Solutions LLC and is made available on the website.
18. How Often the Policy Is Updated
The Policy is reviewed when needed, and the sections that require it are updated.
19. Entry Into Force and Withdrawal of the Policy
The Policy is treated as in force once it is published on the muvcloud.com website. If a decision is made to withdraw it, the earlier wet-ink copies of the Policy are cancelled by a management decision (by a cancellation stamp or by writing that they are cancelled), signed, and kept by the management representatives for at least 5 years.